What is P-SSCRM?
What P-SSCRM is
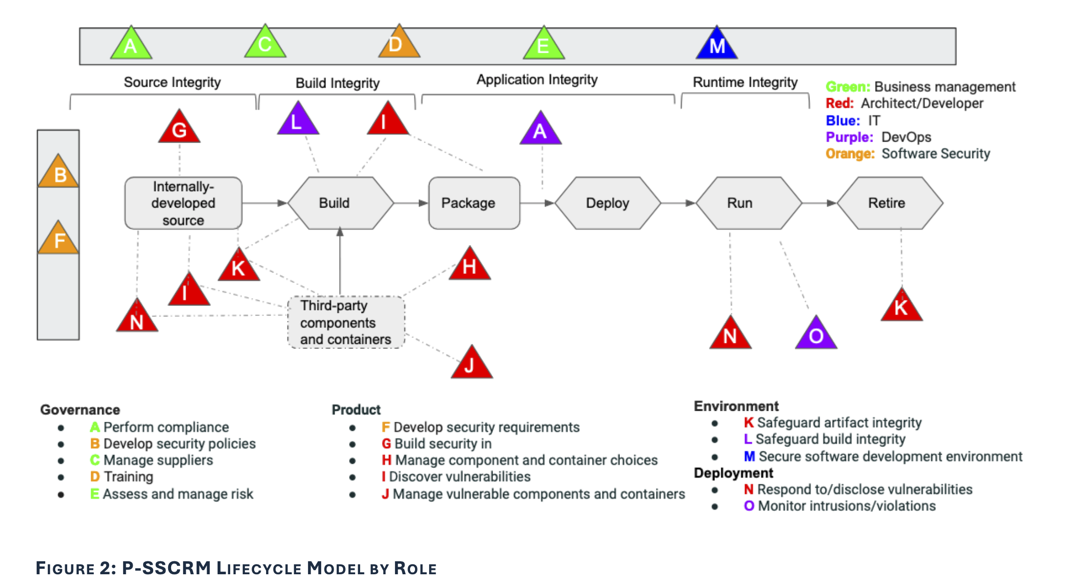
P-SSCRM (Proactive Secure Software Supply Chain Risk Management) is a framework for managing software supply chain security risk. It organizes the work into Groups — Governance, Product, Environment, and Deployment, plus an Unassigned holding group for controls identified but not yet tied to a standard — each broken into Practices and then into concrete Controls. Every control states an objective, a fuller definition, a set of assessment questions, and a mapping to the established standards it draws from.
The problem it solves
Teams trying to secure a software supply chain face a crowded field of government and industry guidance — SSDF, SLSA, BSIMM, CNCF, OpenSSF, NIST 800-161, Executive Order 14028, and more — with overlapping vocabulary and no single through-line. P-SSCRM was built to be that through-line: a single model whose controls are cross-referenced to those sources, so a team can work from one checklist and still show alignment with the standards that apply to them.
How it was built
P-SSCRM v1.0 was authored by Laurie Williams, Sammy Migues, Jamie Boote, and Ben Hutchison.
P-SSCRM was assembled by analyzing the contributing standards and frameworks listed under Standards & Frameworks, identifying the common practices across them, and expressing each as a control with an explicit back-mapping. The framework definition and its mappings are maintained in the open at github.com/p-sscrm/p-sscrm; the MITRE ATT&CK technique mappings are maintained at github.com/p-sscrm/ats-to-ts. This site is generated from those repositories.
Who it’s for
Security leaders
Planning or benchmarking a supply chain security program.
The FrameworkEngineers
Engineers and practitioners doing the work of securing builds, dependencies and deployments.
Which controls apply to me?Assessors
Assessors and consultants evaluating a program against recognized practice.
Assessment questionsResearchers
Researchers and standards authors looking for a consolidated view of the field.
Contributing standards
Citing P-SSCRM
P-SSCRM is described in the paper P-SSCRM: Proactive Secure Software Supply Chain Risk Management, available at arxiv.org/abs/2404.12300. Please cite that paper and link to this site.
Who maintains it
P-SSCRM is stewarded by researchers at NC State University in collaboration with the Secure Software Supply Chain Center (S3C2). For questions or corrections, see Contact.
We welcome the participation and collaboration of all other interested parties.
License
P-SSCRM is licensed under a Creative Commons Attribution-ShareAlike 4.0 International (CC BY-SA 4.0) license. See github.com/p-sscrm/p-sscrm for the framework content. This website’s code is in the site repository.
Version history
Only the version marked current should be used for new compliance work; earlier versions are kept for reference. Data comes directly from p-sscrm/p-sscrm and p-sscrm/ats-to-ts.
Framework
-
Current —
v2.0
(JSON)
Updated SLSA to v1.2, BSIMM to 15, and CNCF SSC to v2; added SSDF-AI; added a more granular mapping of OWASP SCVS; removed S3C2F, which was incorporated into SLSA v1.2. - Previous — v1.0 (JSON)