Measure and Improve
Work is underway to add assessment questions related to AI into controls, as appropriate. Once complete, P-SSCRM v3 will be released, and the research team will begin interview-based assessments. Organizations who participate in an assessment will be provided with a report of their software supply chain security practices adoption, using P-SSCRM as the instrument and following the methodology described in the project paper and a comparison of their adoption versus other companies who have been assessed.
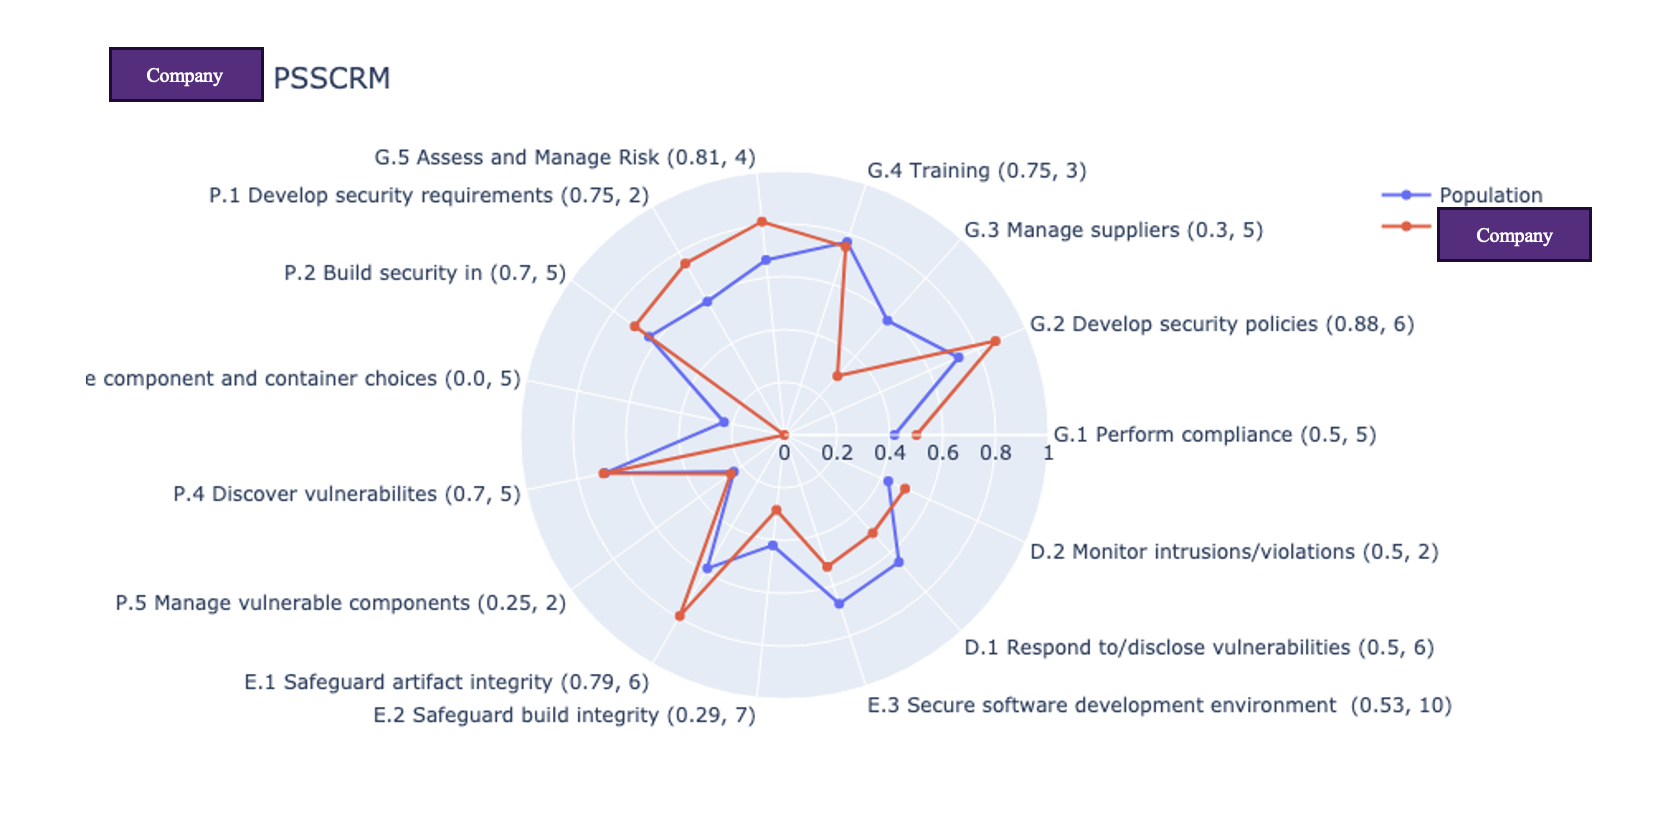
What taking part involves
- Interviews with people who are responsible for the roles for your supply chain governance, secure SDLC, build infrastructure, and release process.
- We walk through the P-SSCRM controls and record how your practices line up.
- You receive a summary of the findings for your organization.
Who should take part
Organizations that build and ship software and want an external, structured read on their supply chain security posture — whether or not you have used P-SSCRM before.
Sign-up Form
Sign-up form — link coming soon
Questions, or want to talk first?
- Laurie Williams — csc.ncsu.edu/people/lawilli3 · lawilli3@ncsu.edu
- Patrick Morrison — linkedin.com/in/pmorrisonfl · pjmorris@ncsu.edu